Preloader

Olympus Blog

In the Olympus blog you'll find the latest news about the community, tutorials, helpful resources and much more! React to the news with the emotion stickers and have fun!

OpenAI agent hacked Australian government website, PM says

Cachella Smith
Live reporter

A headshot of Australian Prime Minister Anthony AlbaneseImage source, EPA

As discussions took place at the UN General Assembly in New York about the opportunities AI provides – and how best to manage it – Australian Prime Minister Anthony Albanese revealed that the country’s universal health insurance scheme had been hacked by an OpenAI agent.

In fact, the hack happened in June, the company became aware of it in August, and then sent an email to a government agency’s general inbox in September.

“It took the company way too long to inform the government,” Albanese said, adding that the method of notifying officials was also “unacceptable”.

Believed to be the first known breach of a government system by rogue AI agents, the hack accessed Medicare’s statistics portal which contains private, but not sensitive, data.

Our cyber correspondent, Joe Tidy, writes that experts believe the systems were poorly protected – but more important is that this is not the first instance of AI agents ignoring laws on accessing online information.

Tech reporter Tom Gerken explains AI itself has no true understanding of what it is being asked – while tech editor Zoe Kleinman asks if AI is in its “move fast and break things” era.

The Australian government has launched an review of AI laws and governance – but this is a global issue.

AI might have dominated discussions at Unga this week, but a consensus among world leaders on how best to harness opportunities while tackling the risks still feels a way off.

Our live coverage is closing now – read our main story here. Thanks for joining us.


Source: Hacker News

Ideas on modernizing the open-source desktop

By Joe Brockmeier
September 23, 2026


Akademy

Scott Jenson has been working on user interfaces (UIs) and user experience (UX)
for many years at Apple, Google, and other companies. Now, he’s trying to convince
open-source projects to experiment more and drive the desktop beyond the age-old “windows, icons, menus,
pointer
” (WIMP) model. At Akademy 2026, KDE’s annual developer
conference, he shared his complaints and ideas in a talk aimed
at convincing those in attendance to take the lead on desktop design.

He introduced himself as someone who has been doing UX for a long time, much
of that time at Google. He said that over that time he had noticed a cultural shift,
“because back in 2005 when I joined, we weren’t evil; we were really trying to do the
right thing
“. He had worked on the Chrome team for a while, which he said was
“filled with people who wanted nothing but open-source, open-web”
projects. Things had changed radically, which led him to leave Google, “but I’m
trying to atone for my sins working for these companies
“.

This LWN.net subscription-only content has been made available to you by
an LWN subscriber. To see more of this content, please take advantage of
the following special offer.

Free trial subscription

Try LWN for free for 1 month: no payment
or credit card required. Activate
your trial subscription now
and see why thousands of
readers subscribe to LWN.net.

He now does work for Mastodon and Home Assistant, “just kind of trying to
squeeze a little bit more good UX design into open source
“. Jenson said he did
not want to be confrontational, but he thought that open source needs a lot of help
in the area of UX design. That is challenging, because open-source projects are
understaffed.

Innovation

He was at Akademy to discuss his ideas because he had given a talk
similar to this at Ubuntu’s conference last year, which proved to be popular. “It
got more than half a million views on YouTube—which by YouTube standards is
trivial, but by Scott standards is enormous.
” That told him that the topic of
desktop UX was something that people wanted to talk about. This time around, he also
wanted to show a few examples of prototypes he had to demonstrate his ideas.

[Scott Jenson speaking]

He thinks that desktop UX is very different from other kinds of UX. Jenson related
a story about working on the Macintosh’s Finder application, which is a file
manager. The team “wanted to do ellipses” in file names when showing a file in
the Finder that had a name too long to display in its entirety. The developers wanted
to put the ellipsis at the end of the file name, but he thought that would lose
too much information, and suggested that the ellipses should be in the middle of the
file names. “It’s now considered to be one of those things that’s an exciting
little attention-to-detail issue the Macintosh does.
“

Another UX detail that he worked on is the way that clicking and dragging files
from one window to another works on the Mac. A mouse click action has two parts: when
the user depresses the button (mouse down) and when the user releases the button
(mouse up). On the Mac, item selection happens on mouse down, but the window only
raises on the mouse up action. In other words, if a user drags an icon from a Finder
window into another window, the first window is not raised.

On most Linux systems, though, if a user is trying to click and drag a file from a
window in the background it will cause the window to raise as soon as the user does
the “mouse down” action. That complicates trying to click and drag a file from one
window to another. That is a fundamental action that means that users can’t move data
into applications quite as easily on Linux as they can on the Mac.

He said that he had talked about that issue two years ago on Mastodon, which
raised a response from a KDE developer who thought it was a good idea to separate the
mouse down and mouse up actions when dragging data between windows. Then they
implemented it a few hours later.

“I forgot who that was. So if anybody here did that“, he said, but before
he could finish the sentence a voice from somewhere in the room responded, “you’re
welcome
“. Jenson yelled “thank you! I’ve been wanting to meet you for two
years!
” That was an example, he said, of how open source can be awesome:
someone can just say “that’s a good idea, I’ll just do it” and then rapidly
implement and push the feature to the project.

Stabilized

The point he was really trying to make, though, is that the desktop UX
had not really changed in 20 years. There were plenty of new ideas and improvements in
the 1980s and 1990s, “and then it just stabilized, and not much has really
changed
“. But people are doing much more with their computers today, and he
thinks that there are ways for desktop UX to grow.

Much of the UX for Linux systems was originally copied from Windows and the Mac,
“KDE even says it’s for Windows users, that it wants to be similar to Windows for
users
“. There’s nothing wrong with that, but he felt that the Linux community
“in general” had been leaning on Microsoft and Apple to do all of the UX research
and testing, “and frankly, [make] the mistakes“.

Some might point out that GNOME has conducted
user research
for some of its design changes, and KDE’s human-interface guidelines (HIG) were also developed based on research by its
contributors. However, it would be fair to say that these are exceptions rather than
the norm; certainly, no one is funding or conducting regular UX design research and
development for the Linux desktop overall.

He said that it is smart to let Apple and Microsoft do these things first “so
we can draft behind them
“, but the problem is that “they’ve just kind of given
up to an extent
“. Apple has been letting its desktop UX, and desktop hardware,
“languish for years and years and years” because it had shifted its focus to
the iPhone and iPad devices. “I mean, like, Apple wanted the Mac to die. They
wanted the world to move over to the iPad. Guess what? It
didn’t.
“

Apple has since turned its attention back to the Mac, but the things they’ve done
since—such as the Liquid
Glass design language
—have not been really popular with users. The features
that Apple tends to add, he said, are “basically about tying it closer to the
iPhone, tying you closer into their ecosystem
“. That isn’t about improving the
desktop, it’s about increasing their moat.

Microsoft “is just making one mistake after another“. He cited the
company’s attempts to force users to store files using its OneDrive cloud-storage service, the
privacy-invasive Windows
Recall
feature that drew widespread criticism, and “ads everywhere” on the
Windows desktop. His point was not to bash Apple or Microsoft, though the audience
didn’t seem to object to this, it was to point out that the Linux desktop could not
follow their example any longer. “The whole Linux community has been just waiting
for Apple and Microsoft, more or less, to take all the risks, and they’re not taking
any more risks.
”

Three pushbacks

Jenson emphasized that he didn’t want to change everything, but he wanted to see
experiments and additional development aimed at improving the desktop
experience. However, he said that he gets pushback when he tells people that desktop
innovation has stopped, and that the Linux desktop “can’t just patch and bug fix
our way into the future, we have to start taking leadership ourselves
“.

He grouped the pushback into three categories. The first objection he receives is
“mobile won; the desktop is old, just do what mobile does“. He dismissed that
by saying that mobile has indeed won the consumer market, social media, and other
areas, but “it didn’t win productivity“. People still do their work on
computers, because “desktops are silently awesome; they have keyboards and big
screens, and they can do amazing things
“. However, people have lost sight of that
and don’t really appreciate how good desktops are. “I think we should understand
why they’re good, and then what we can do to make them better.
“

The second objection he hears is that there are only so many ways that the WIMP
model can work. “Just stop trying to fix it; it’s done.” He disagreed with
that as well, and thought that there was more to be done. The final, particularly
strong, objection from the tech community is “don’t touch my stuff“. People
get angry when they have worked hard to get their desktop environment just as they
like it and something changes to disrupt that. “And I get that. As I said before,
I don’t want to change everything.
” But the world is changing, “and we need to
grow our way gently into some new things.
“

What is UX?

Thinking about where to go next with desktop design gets to the question “what is
UX?” He said that term was misunderstood and that people, especially manager types,
“they think it’s just pixels, but UX is so much more than pixels“. It helps to
think of UX as having layers, he said. There is style, which consists of white
space, iconography, color schemes, and yes, pixels. But there is also structure, he
said, which is how the user moves through the application, the navigation
model.

Strategy is another part of UX; understanding who the target user is, and
determining what they want. Deciding what is important, and what is not; what will
the development team prioritize and what will it ignore? “The fastest way a UX
designer can save your team time is to help you say no.
“

There is also a layer he called “stuff“: the lower-level limitations of the
underlying technology that a platform has which influence UX. For example, he said, if
an application is being created for DOS, “you’re not going to write a nice
Macintosh application. The technology dictates what you can do
“. The desktop has
been evolving for 40 years and has “historical cruft” that carries expected
standards.

We just have a bunch of stuff that we just accepted. And I think if
we’re going to fix the desktop, we have to understand this lower-level limitation,
and how do we want to fix that? We just accept that mobile and desktop has stuff
today, and we just don’t think about fixing it.

People forget, he said, that the original Macintosh screen was “a whopping 342
pixels high
“. Naturally, windows overlapped a lot. Since then, “we just
assumed that Windows have to overlap
“. But many people have “giant, giant
screens
“, and the existing window-manager model does not work so well for those
devices. “I can understand why people use tiled window systems and so forth,
because this existing model just does not work very well.
“

Understanding the future

Early in the talk, he had referenced a saying by Alan Kay, who had led design of the
first WIMP interface at Xerox PARC: “Perspective is worth 80 IQ points.”
Jenson now circled back to Kay: “Who, as you can tell, I really like a lot. […] He
talks about three steps to understand stuff
“. The first step, he said, was to
think about the present, “what is happening right now?” The second is
“don’t forget the past, know what work has happened before“, and the final
step is to ensure that “your questions are really clear“. Too many people rush to
a solution, he said, but they should be rushing to questions. If the questions are
clear, then the answers will be better.

He did not want to make the talk about AI, he said, but he had to address
it. “I have to talk about AI, and it pisses me off because there’s so many cool
things we could be talking about, and AI just sucks up all the oxygen, and it’s all
you can talk about
“. But, he conceded, there are many things happening with AI on
the desktop, albeit in a weird way.

He explained some of the current efforts to integrate AI with the desktop as
“trying to sneak AI in” while keeping the UI exactly the same. Other efforts
try to use AI to understand what is on the screen and use chatbots to interact with
the interface, “which I think is kind of missing the point here“. That is,
until last summer when Anthropic introduced Claude Code. “It completely changed
things, because was looking down into your filesystem
” and drew context from the
content of a user’s files. That allowed it to do more interesting things and interact
with the system.

After mentioning Claude, he paused to say he was only speaking about frontier
models because everyone else is discussing them. “I have a lot of personal
problems with the frontier models. They are ethical and environmental disasters. I am
not very excited by them
“. He said he was excited by Apertus, which is billed as a fully open,
responsible model for sovereign AI created by the Swiss AI Initiative. “I do think it’s
possible to talk about ethically trained small language models running locally, and
you don’t have to sell your soul to the devil.
“

The curse of direct manipulation

The key point he wanted to make was not about generative AI uses, but about how
giving it access to the filesystem improved its usability. It now had context and
could work with the user’s data, but it was working at the filesystem level and not
using the desktop UX.

He talked about the desktop building blocks, basically the familiar WIMP model
plus the desktop clipboard, as the way that users move data around. Expert users
can move data around quickly, he said, but there’s a problem: the desktop is
stateless. He called this the curse of direct manipulation; there is no working
memory to the desktop. “If you copy a few too many things to the clipboard, oh
sorry, it’s gone
“.

Jenson theorized that the reason there are so many desktop environments, window
managers, and Wayland compositors for Linux—as well as alternative clipboard
managers—is because the desktop isn’t quite working right for users. He thought
it was really about working memory: “How do I manage my data in such a way that I
can remember it across all of these things and actually use it.
” His perspective
shifted to asking “what would we do to working memory to improve the desktop
UX?
“

AI may have given him the idea, but he added that he wanted to solve the desktop
UX for people first. “If the AI can use it, great. I don’t care. That comes
later.
“

Remember your past

There is prior art in trying to create systems that help provide users with more
context and working memory related to their data. He referenced a paper called
“Lifestreams: a storage model for personal data”. That paper made the case that
desktop systems are “are ill-equipped to manage the electronic information and
events of the typical computer user
“, and introduced the Lifestreams idea as a
metaphor for dynamically organizing a user’s computer workspace.

That paper influenced the ill-fated WinFS project from Microsoft, which
was an attempt to merge data storage and management based on relational database
systems. It was demonstrated in 2003 and scheduled to ship sometime later, but
ultimately the project was shelved in 2006. On the free-software side of the house,
there was the semantic
desktop
project NEPOMUK,
which was a research project funded by the European Union.

A version of NEPOMUK was included
in KDE 4
, with the idea was that it would allow applications “to use
information from all over the desktop, the web, other devices, and combine it into
one coherent interface
“. It was later removed and replaced with the Baloo file-indexing and search framework
for the Plasma desktop, which has some overlap with NEPOMUK’s functionality but with
a reduced scope of features.

Jenson said that he is concerned that people see the failure of those projects as
proof that the ideas were wrong. He argued that is not the case, “I would say that
it is the hardware and systems at the time let the vision down. I think it’s time to
rethink these projects
” in light of newer hardware and better systems.

Prototypes

Having visited the present and the past, as Kay recommended, he had come up
with a few questions that he thought worth exploring related to desktop UX. The first
was “what would happen if we only designed for large monitors?” What would it
unlock if there were desktop designs that ignored laptops and only focused on
widescreen monitors? Another question he had was how could the desktop capture a
user’s intent over time?

Those questions led to the prototypes that he said he was a little nervous to show
the audience “because technical people love to find mistakes“. The demos are
about 29 minutes into the video
of Jenson’s talk
. His slides have not yet been published but he told me at the
event that they would be at some point.

The first demo was to show how a desktop might make better use of a widescreen
display. He noted that the center of a widescreen monitor is good for working
with an application, but it becomes more difficult to work on the sides of the
monitor. “It’s good for peripheral vision, but not good for working“.

He demonstrated a desktop layout, a screenshot of which is below, that would put the
focus on the window or windows in the middle of the monitor. He had included a grid
in the background that tapers off from the middle of the screen to simulate a
widescreen monitor. The idea was that a widescreen-first desktop would emphasize
information in the middle of the screen, and then use an Exposé-like tiling model to arrange the
rest of the desktop’s windows. This would make the windows that were not in use
easier to interact with, he thought, and be a better model than virtual desktops for
managing lots of windows. “I’m not against virtual desktops. Virtual desktops are
used by very organized and intelligent people. I know my audience.
” However, he
said, most people can’t deal with virtual desktops.
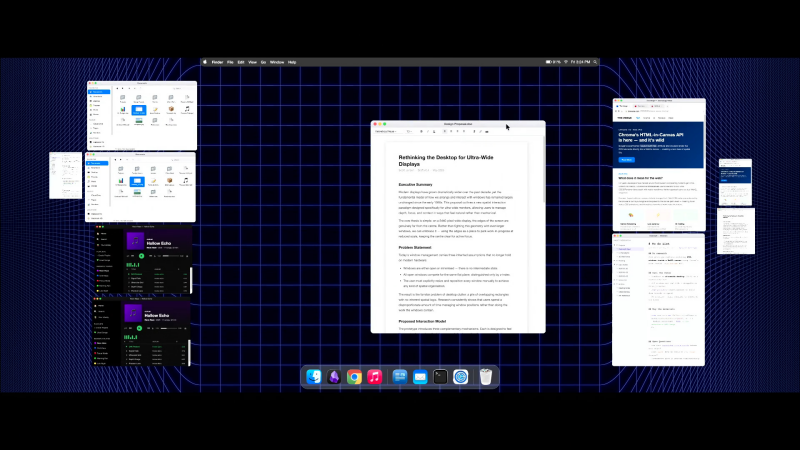

[Window manager widescreen demo]

He also demonstrated dragging a music-player window all the way to one side of the
screen, which he called “the stash area“. As it moved to the edge, it
transformed into a widget with just a play button instead of showing the full
window. He thought that it would be possible to do the things he was demonstrating
with Wayland as it is today.

Jenson put up another demonstration of an improved clipboard model that copied
ideas from the Obsidian editor’s Canvas feature. Canvas allows users to drag and
drop images, text, and files to create a visual layout of information. A user could
create a document and drag information from a web browser into the document, drop a
file in from another source, “the idea here is that this is now effectively a
collection of stuff that I have gathered for this document. And if I close it and
then come back tomorrow, it’s all still there
“. He added that a local AI would be
able to come in and organize the information a user had gathered, “oh, look,
you’ve got a bunch of hotels, let me organize them for you
“.

The final idea he discussed was a way of gathering “privacy-preserving
data
” to help give users a better visualization of things like web-browsing
history. A web browser will only give the user a view of their browsing history that
“is not very useful” he said, so he tried to gather data “not using AI,
just using simple math
” that would use attention signals—such as how long
the user was on a web page—to tell a story of where they spent their time on
the desktop. “I basically came up with this spatial associative episodic memory
prompt
” to organize data in a helpful, interesting way. He thought that working
memory was a good way to explore new ideas for desktop UX.

So the goal with this talk is to say, let’s start to take this apart. And I really
hope that my prototypes cause you guys to come to me and say, We forgot about this,
and let’s talk about that. […] So I just want us to try, because no one else is
going to try, and I think someone’s got to start.

There was time for a single question. An audience member asked how Jenson’s model
would protect against all of the privacy concerns that Microsoft faced with Windows
Recall. “How are we going to make sure that this history remains only accessible
by the user and cannot be hacked in like it could happen with Windows
Recall?
“

Jenson answered that his idea was to gather telemetry data, “not interesting
information
“, which would significantly reduce the attractiveness of the data to
would-be attackers. He said he did not want to underplay the issue, though, and
wanted to build prototypes to see if the idea was good first, and then explore ways
to encrypt or protect the data. He agreed that even this data could be valuable
information. He added that the biggest problem with Windows Recall was “how
stupidly they protected it
” and he was sure others could do a lot better job.

[I would like to thank the Linux Foundation, LWN’s travel sponsor, for its
assistance with my trip to Graz, Austria for Akademy 2026.]

Index entries for this article
Conference Akademy/2026


Source: Hacker News

Police ID man found dead in 1982, cite possible Tylenol murders link

Sept. 23 (UPI) — Authorities in Idaho have identified a man found dead from cyanide poisoning in a Boise church more than four decades ago and believe he may be connected to the infamous Chicago Tylenol murders of 1982.

The man known as the Unknown Wanderer has stumped detectives for years. He was found dead Dec. 4, 1982, inside Sacred Heart Catholic Church with no identification, an envelope containing 19 $100 bills and a typed note signed Wm. L. Toomey and two key rings with nearly 30 keys. His hair had been dyed, his nails were finely filed, his skin was unseasonably tanned and his pants were either brand new or recently pressed.

The case went cold until 2019 when Ada County Detective Tim Cooper reopened the case after a member of the church asked him about it while he was sitting in his car drinking cheap gas station coffee in a parking lot.

On Wednesday, Cooper identified the Unknown Wanderer to reporters during a press conference as Dr. Mathew Betkouski.

Cooper said the break in the case came from one the keys they found on Betkouski’s person, which indicated it was from a Jacksonville, Fla., hardware store. Etchings on a second key led detectives to Jacksonville’s Mills Court road.

After acquiring the property deeds for the street going back to the 1970s and 1980s, one person stood out to detectives — a man who had been pronounced dead in absentia in 1989. The Ada County Sheriff’s Office contacted the decedent’s only living relative who said that his brother had gone missing in 1982.

A DNA sample collected from the man showed that there was a “very high probability” that they shared the same father, Cooper said.

“So, the Unknown Wanderer was determined to be Dr. Mathew Francis Betkouski,” Cooper said, adding that amid the investigation they learned that he had worked at two drugstores during his undergraduate studies and had a history of volatility, including a documented fascination with cyanide and explosives.

In the late 1970s, while Betkouski was working for a flavors and fragrances company in the Jacksonville area, colleagues became concerned about him after he discussed “the perfect crime” and how “cyanide could be used as a less messy means of taking one’s life,” Cooper said.

“Dr. Betkouski was observed talking to himself on occasions and had fears that he was being tracked,” Cooper said.

Writings by Betkouski found by detectives show that he tried to manage schizophrenia and depression and feelings of euphoria brought on by imaginary thoughts of violence.

In late 1979, he was hired by Lockheed where a fellow employee recalled Betkouski stating that poison could be introduced into over-the-counter capsules, according to Cooper, who said Betkouski was fired in March 1982 after creating an unspecified disturbance at a Las Cruces, N.M., area pharmacy as he tried to acquire some kind of pills or capsules he said were for an experiment.

Betkouski’s whereabouts after that date are not fully known and Cooper said they have not been able to place him in Chicago in September 1982, when at least seven people, including a 12-year-old girl, in and around the Windy City died after consuming potassium cyanide-laced Tylenol.

Detectives found pictures of Betkouski in Chicago, but they believe they were likely taken in December 1981. He was last known to be in Las Cruces on Oct. 15 and was next found dead at the Boise church.

“So, where this leaves us is while our office may have identified some possible connection between Dr. Betkouski and the 1982 events, we’re not naming him as a suspect and we cannot say he was in Chicago during the final week of September 1982,” Cooper said.

“More information does exist in this case that we won’t be releasing today.

While Cooper was restrained, Dr. Park Dietz, renowned forensic psychiatrist who was consulted during the initial Tylenol murders investigation and who was brought into the reopened case in 2021, was confident that Betkouski was likely responsible.

“It’s an extraordinary thing to have been around at the beginning in 1982 and now, today in 2026, see very likely closure, that the identity of the Tylenol killer from 1982 can be shared,” Dietz said.

Dietz told reporters that they presented information about Betkouski to groups of forensic psychiatrists, forensic psychologists and criminal profilers, who overwhelmingly considered Betkouski to be a viable suspect, while some “were as convinced as I that Detective Cooper had solved the most important unsolved murder of my lifetime, the Chicago Tylenol murders.”

The Ada County Sheriff’s Office said it has shared its findings with the Chicago Police Department and is calling on members of the public with information about Betkouski to contact the office as investigators seek to determine his whereabouts from Oct. 15 to Dec. 4, 1982.

The developments and yet-to-be-released connections between Betkouski and the Tylenol murders are to be the subject of an Unsolved Mysteries documentary titled Unmasking the Tylenol Killer, which is to air on Roku Oct. 9, saidAda County Sheriff Matt Clifford said during the press conference, explaining that authorities are hoping the exposure will generate more leads.

“Detective Cooper has done amazing work, but there’s still a lot of questions we don’t have answers to,” Clifford said.

“And that’s part of why we’re standing here today. I’m not going to beat around the bush with everybody, but this isn’t over.”


Source: U.S. News

The Year of Internal Tools

Code and Coordinates

engineering at Geocodio

The year of internal tools

How Geocodio went from bash scripts to full internal apps, the system that keeps them maintainable, and where we draw the line between building and buying.


By Mathias Hansen

At Geocodio, it has always been important to us to automate processes and build our own tools and helpers, so we can save time and be more efficient. For almost ten years, Geocodio was just the two of us. Automation is a big part of what made that possible.

Those tools have saved us countless hours over the years. Local bash scripts that set up a development environment or download the specific data files we need for geocoding. Infrastructure scripts that check the health of the load balancer or sync some data down. Small scripts that make the on-premises release process faster and more efficient, with fewer manual steps and less room for human error.

One of the bigger ones came along well before the AI era. We built our own deployment tool. It visualizes the deployment process, so we can easily see how far along a deploy is and what is live right now. If something goes wrong we can see it and roll back. It handles deployment freezes and a bunch of other things that would be a lot more cumbersome and a lot less transparent as a manual process.

The deployment tool, showing the public cluster with every node on the latest release and the deploy dialog open

The deployment tool. Every node in the public cluster is marked with the release it is running, and the deploy dialog lets you pick a scope and post the result to Slack.

All these small scripts and helpers and various tooling have been helpful over the years and have had a positive impact. But it pales in comparison to where we are at in 2026 and what we are able to do now.

What changed

This is the year of internal tools. We have gone from creating small bash scripts here and there, artisan commands in Laravel, small isolated repos with code to generate reports, to being able to really raise our ambitions and create full-fledged internal apps. Mobile friendly, good UX, fantastic test coverage.

What allowed us to do that is the advent of AI and frontier models that let us build at a much higher level than we have ever been able to before.

I must admit that in the beginning I was hesitant to start taking on these larger projects. The thing that always got in the way of the bigger, more ambitious ideas was not the building. Even pre-AI you might be able to knock out some kind of awesome internal tool over a couple of days. But then you have the maintenance burden. You cannot keep building tools if you do not think about the fact that you have to maintain them, keep them working, keep them up to date, fix the bugs you find.

That is the other side of the coin, and it is the side AI has also allowed us to solve. I am not worried about building all these internal tools and maintaining them, because I can use AI to keep up with the maintenance as well.

We have a system for it now

We have gotten to the point where we have specific systems in place that let us quickly scaffold and create a new internal tool. We recently launched our console-ui package, which includes Tailwind CSS tokens as well as shared React components, so all these internal apps share one component library instead of each one growing its own.

We have also built up enough experience with AI that we have some solid principles for how to give these tools a strong foundation, so they are built for the long term:

  • A significant amount of planning before we take on the job of building anything.

  • A lot of research, including engineering spikes that prove out a concept first.

  • Numerous Grill Me sessions, using Matt Pocock’s wonderful Grill Me skill, which interrogates a plan until the weak parts fall out.

  • Iterating on UI mockups, which answers a surprising number of questions and resolves problems before we go and build the real thing.

  • Using powerful models like Fable in the planning process, to make sure what we are building solves the problem we are trying to solve, in a sustainable and well-engineered way.

On top of that, we have also built up high quality internal standards for these projects. Testing, CI, static code analysis, best practices for authentication, that kind of thing.

That is also where the time goes. The planning and the spec take weeks. The implementation takes hours or days. Some of these apps we had been thinking about for years before that, so the spec was mostly a matter of collecting what was already in notes and meetings and turning it into a project. Atlas is the clearest example. It had been in my head for years, and once the spec existed, building it was the fast part.

Every tool ships with its own documentation

Each of these tools has a full documentation subsite. A real guide on how to use the tool and how each feature works, with screenshots and examples.

The Bullpen documentation subsite, with a user guide and internal docs section and a page explaining what Bullpen is

Bullpen’s documentation subsite. Every tool has one, split into a user guide and internal docs.

A lot of it is AI-generated, at least the initial draft. Even so, having that consistency across every tool is really nice. It communicates what a tool does and how to use it much better than a README ever did.

It also solves a problem I did not expect. When you have been sitting there writing big specs and plans for weeks, you sometimes lose touch with what you built. Writing the documentation brings that back into focus.

Every one of these repos has a rule in its CLAUDE.md saying that any change affecting the documentation requires Claude to go and update, add, or remove the relevant parts. It still needs a human eye here and there, but it is a solid base rule that keeps things current. Documentation that is not up to date is useless.

This is the rule from the Atlas repo, lightly trimmed:

CLAUDE.md

### Keep both sections in sync with the app

Whenever you make a material change you MUST update the documentation in the same change.
A user-visible change lands in the user guide; a change to architecture, dev
workflow/tooling, infrastructure, deployment, integrations, a pipeline/job/schedule, a
scheduled command, a deploy/secrets change, or an Environment API contract bump lands in
the internal docs. Many changes touch both.

- **Changed behavior** → edit the relevant page(s) so they describe how the thing actually
  works now. Don't leave stale screenshot markers, steps, class names, paths, commands, or
  claims.
- **New feature or new maintainer-facing surface** → add a new `.md` in that
  section's directory and register its slug and title in the matching `DocsManifest`
  constant. The manifest is the single source of truth for which pages exist, their order,
  and their sidebar grouping.
- **Removed capability** → delete the page **and** its manifest entry, and any cross-links
  to it from other pages.
- **Renamed/moved** → update the slug in both the file name and the manifest, and fix
  inbound links.

What we have built

We are taking on bigger challenges now, like building our own customer support platform.

  • Atlas for customer support. It is built, and we are rolling it out now.

  • Bullpen for managing, organizing, and planning our sprints.

  • Yak, a coding agent for papercuts. It picks up small tasks from Slack, Linear, Sentry, and GitHub and comes back with a pull request to review. Yak is open source, so anyone can download it and run it against their own repos.

  • Our deployment tool.

  • A compliance tool that covers the parts our compliance platform cannot do, and then pushes the results back into it.

  • Treehouse, which gives every git branch its own worktree and its own docker-compose stack, so several branches or agent sessions can run at once without colliding on ports. Also open source.

Yak showing a completed task: the request from Linear, a summary of the change, the activity log, and a recorded walkthrough

Yak, after finishing a task that came in from Linear. The request, the summary of what changed, the step-by-step activity log, and a recorded walkthrough of the result.

Our infrastructure engineer is also working on a tool for managing infrastructure, handling CVEs in our dependencies, and making regular maintenance easier with CD jobs on top of GitHub Actions. That one is a good illustration of the maintenance point above. Some of the tools exist to keep the other tools healthy.

Why the support platform is worth building ourselves

The big benefit of building our own is that we can make it extremely well integrated with our workflows and our data.

Right now, helping one customer can mean going into three or four different tools to get the information you need. Our current support tool. An admin tool, and we have two of those, one for self-service and one for enterprise. The billing tool. Analytics. Having both self-service and enterprise customers makes the picture more complex for us than it would be for most companies.

The whole point of building the support platform ourselves is to bring all of that into one place. The person replying to a customer can see exactly what is going on with that customer, what kind of account they have, and what has happened recently, in a UI that is streamlined for the exact workflow we have at Geocodio. They get the information and the actions they need at their fingertips, which means we can solve the problem much faster.

What we are not going to build

None of this means we are going to replace every SaaS product we use with our own tool, or that we are going to go build dozens of new internal apps. There is a limit, and there is a fine line between what should be in-house and what should be off the shelf.

Email stays with Bento, and we are happy with it. Running our own email infrastructure is a responsibility that makes no sense for us to take on. The risk is too high, and it is not something we have any experience with. Twilio keeps the communications work. Nobody here is writing a Slack. There is plenty of good tooling out there.

Three questions sort it for us:

  1. Do we have real experience in this domain, or would we be learning it on the job?

  2. What happens to the business if this is down for a day?

  3. Does the value come from being integrated with our own data and workflow, or would an off-the-shelf tool do the job just as well?

Just because tools are easier to maintain now does not mean we can take on fifty of them. We have to be deliberate and thoughtful about the way we build them. This is also why we build them on shared infrastructure, shared UI, and shared principles, so they are easier to maintain and share as much code as possible. We are not trying to create a micro-internal-tool-services architecture either. We want tools that cover a whole feature set, rather than inventing a new service every time we have an idea.

Every tool you build is a responsibility

That trade-off is real each time, and the part that is easy to forget is uptime. Internal tools need to be reliable too. What would happen to our business if we could not reply to customer support requests for a day because we shipped a change and broke something?

We got a small taste of this recently. We have an internal ETL tool for importing and working with address data. We did a massive upgrade of it, and then it was unavailable for a day while we ironed out a few issues with the deployment. In this case it did not affect keeping the lights on. If the same thing had happened to Atlas on a busy day, it would have been a different story.

That day was the result of a trade-off we made on purpose. These tools do not have a staging environment. A staging environment for every internal tool is one more thing to keep running and keep in sync, and for tools that only we use, we decided that cost was not worth paying. Changes go to production, and local QA, test coverage and CI carry the weight that staging would otherwise carry. The ETL outage is what that decision looks like when it goes wrong, and we accepted that when we made it.

The other half of the responsibility is access. Atlas can see customer accounts and billing, so who can reach it matters as much as whether it is up. One big benefit of hosting these tools ourselves is that they live entirely inside our private network. They are not reachable from the public internet at all. You have to be on our VPN before the sign-in page even loads, and only then do the usual authentication rules apply.

Where this leaves us

I do not know what the future will bring. We have to be careful not to end up maintaining tons of internal tools, or creating tools for the sake of creating tools.

But if these tools help us do our work better, make us more efficient, and reduce the chance of human error from manual processes, then we can build a better product, we can give our customers a better experience, and we can improve the quality of life for our team.

If you are thinking about this at your own company, start small. Find the process where you already work around the gap between two tools by hand every week, and build the thing that closes it. That is where we got the most value the fastest, and it does not require you to believe that anyone should rebuild a SaaS product from scratch.

Get new posts in your inbox

We write about what we’re working on, thinking about, and getting so excited playing around with that we accidentally stay up a bit too late.

Thanks for subscribing!


Source: Hacker News

Judge orders Trump to restore CNN, MS NOW, Politico press access

Sept. 24 (UPI) — A federal judge early Thursday ordered the Trump administration to reinstate CNN, MS NOW and Politico’s White House access, temporarily blocking President Donald Trump’s ban of the three media organizations.

The Trump administration has taken a hard-line stance against media outlets whose coverage it criticizes and has taken numerous actions during its second term to restrict their access, including taking control of the press pool that has access to Trump.

Trump banned the three news outlets on Friday, calling the outlets “FAKE NEWS” on his Truth Social media platform, prompting the trio to sue, alleging their constitutional rights had been violated.

Judge Timothy Kelly of the U.S. District Court for the District of Columbia ruled in the news organizations’ favor early Thursday, issuing a temporary restraining order that directs the Trump administration to reinstate their hard-pass press credentials for 14 days, unless the court orders otherwise as litigation continues.

In his ruling, Kelly, a Trump appointee, said the news organization were likely to succeed in showing that they were banned “without constitutionally adequate due process.” Because substantial interests are at stake, the government must provide clear standards for conduct that would lead to ban and give reporters fair notice of both the prohibited conduct and possible penalties.

“None of defendants’ arguments convince the court that plaintiffs are not likely to succeed on their due process claim,” Kelly said, adding that the Trump administration had not shown why a ban was urgent as the reporting it identified were published months and years ago, and the activity it cited was “routine.”

Kelly also said that the court was skeptical of the Trump administration’s defense that the ban was in the interest of national security, saying it had offered little evidence to support its claim.

“For one thing, nothing in the record that predates this suit suggests that the revocation of plaintiffs’ hard passes was motivated by national security concerns,” Kelly said.

“Certainly, that is not what President Trump said when he announced that he was ‘banning’ plaintiffs from the White House — instead, he focused on the alleged lack of truthfulness and negativity of plaintiffs’ reporting.”

Ted Boutrous, a lawyer representing the outlets, told CNN that they “greatly appreciate” the court’s swift order.”

“This is a strong ruling vindicating freedom of the press, due process and the rule of law,” Boutrous said.

This week in Washington

President Donald Trump speaks to more than 100 hunters and fisherman at a dinner in the Rose Garden of the White House on Thursday. Photo by Jim Lo Scalzo/UPI | License Photo

Source: U.S. News

Meet the real-life Pokémon professors, the unsung heroes of competitive monster-battling

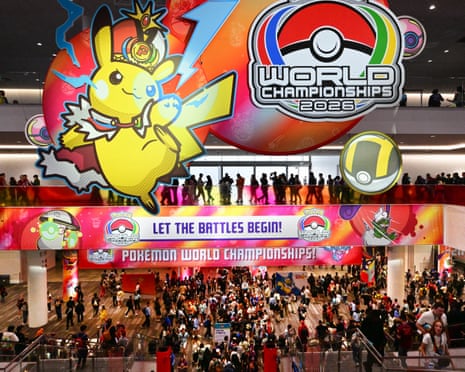
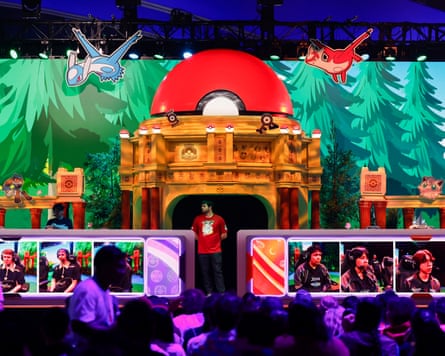
Crowds fill an escalator area beneath giant Pikachu and Poké Ball decor at Pokemon World Championships

Let the battles begin … people attend the 2026 Pokemon world championships in San Francisco, California. Photograph: Frederic J Brown/AFP/Getty Images

Let the battles begin … people attend the 2026 Pokemon world championships in San Francisco, California. Photograph: Frederic J Brown/AFP/Getty Images

Meet the real-life Pokémon professors, the unsung heroes of competitive monster-battling

They offer advice, referee card games and manage players’ tantrums – we caught up with some of the volunteer profs who keep the competitive game going at this year’s world championships

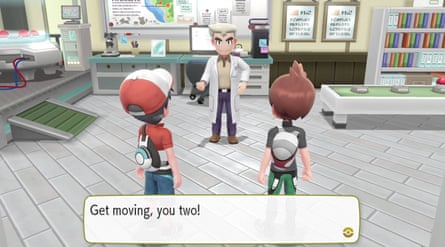
Professors may be the most revered characters in the fictional world of Pokémon (apart from perhaps the Gym Leaders). In Pokémon Red and Blue, Professor Oak greets the player in a pixelated lab coat, and later provides trainers with their first battle partner; since then, each successive generation of games has introduced another professor to aid and guide trainers through their journeys. If you’ve ever played a Pokémon game, they are often the first people that you meet, apart from your in-game mom.

But you may not know that there are also real-world Pokémon professors – volunteers who help organise the game’s competitive communities around the world. Instead of lab coats, they can be seen at events wearing red Pikachu-mascot shirts labelled “staff”, paired with black trousers and shoes.

I spoke with several of these profs at the 2026 Pokémon world championships in San Francisco, California. Not only do they happily distribute their knowledge about Pokémon, but they also serve as vital staff at the tournament, working as referees and teachers, as well as event managers.

The official Pokémon website describes the Pokémon Professor Program as a “global network of passionate and knowledgable fans” who volunteer their time to help run official Pokémon events. There were roughly 300 Pokémon professors present at the 2026 Pokémon world championships, according to a representative of the Pokémon Company International. A professor’s responsibilities depend on the game they work with and their assigned role at the event. A Pokémon professor officiating a game such as Pokémon Unite might be hyper-focused on wrangling players and providing technical support, whereas a judge for a trading card game tournament might provide competitors with hands-on guidance as they navigate their first live competitive event.

The OG Pokémon prof … Professor Oak in Pokémon: Let’s Go, Pikachu! Photograph: The Pokémon Company/Nintendo

Gemma Byard, a head judge in charge of making the final call on any decisions or questions that arise, became a Pokémon professor after her son started competing in the trading card game. She says that she and the other professors help ensure the integrity of the tournament, describing what goes into the day-to-day work at worlds – such as ensuring that event officials record the results of competitions correctly.

“We’ve got to make sure that all of the match slips have the correct results on them and are signed by the players to ensure, you know, that we get the right results,” Byard said. “We have to make sure that the venue is safe for everybody that’s around. We’re constantly looking out for anything that may be unsafe, or anybody that shouldn’t be in the venue. There’s a lot to think about on top of the rulings.”

Professors often juggle multiple responsibilities on the competition floor and will travel across the world to staff an event such as the world championships. When asked about how the Pokémon Company International compensates its professors, however, most people I spoke to declined to disclose details. One Pokémon professor said that the European professors are compensated with goodies, such as a special staff kit with merchandise, whereas the professors at regional tournaments in the US are paid wages; the same professor said that the Pokémon Company International helped with travel, room and board for the event. (When asked for an official statement explaining how Pokémon professors are paid, a representative from the Pokémon Company International declined to comment.)

Evelyne de Groot travelled from the Netherlands to staff this year’s championships. Like the other Pokémon professors I spoke to, de Groot worked her way up to staffing worlds after organising local competitions in her home region. Before we spoke, she was helping usher players out of the Moscone Center after the main convention hall closed for the evening. This year, she worked at a trading card game side event called Pokémon Sisterhood League, dedicated to giving women and non-binary people a chance to compete and connect.

Passionate and knowledgeable …about 300 professors were working at this year’s Pokémon world championships in San Francisco. Photograph: San Francisco Chronicle/Hearst Newspapers/Getty Images

For her, a good Pokémon professor must balance enforcing the rules with giving competitors the tools they need to enjoy the game itself. She compared the position to working in “customer service”.

“[Players] make friendships. You see them smile. You see them have a good time, but you’re part of that,” de Groot said. “If you’re not organising it properly, if you don’t give them clear instructions, then you see some failure […] You will sometimes get questions. You need to make sure you’re knowledgable regarding that. If you don’t know what you’re doing, if you don’t know how the card game works, then you can’t help them.”

De Groot’s experience as a professor has been relatively relaxed. However, some professors must serve as referees and make contentious calls throughout the competition. For Byard, that means she sometimes needs to deal with upset players. At one point during the tournament, she had to manage a player who was upset with a ruling that didn’t go his way.

“I got called over to the table, and I said to him: ‘Look, I need you just to keep your voice down and be respectful, and we’ll talk through what’s happened.’ And he was like: ‘I don’t need to talk to you. I need to talk to the head judge,’” Byard said, chuckling. “Well, buddy, you are talking to the head judge. That’s the kind of sass that we deal with a lot.”

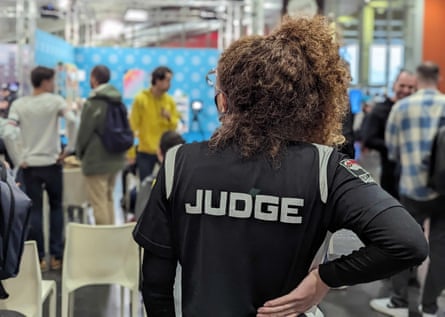
Tough calls … a judge surveys the scene at a previous Pokémon event. Photograph: Pokémon

A difficult call can lead to controversy. Earlier this year, a ruling from a different judge at another tournament made headlines when a competitive Pokémon Go player who goes by the name Firestar73 was disqualified after winning the final at the Pokémon Orlando regional championships. Many, including the competitor himself in a statement, conceded that the decision was a “good-faith mistake”.

I asked Byard about what it’s like to make tough calls at the tournament. She said that the professors are often seen as “the bad guys”. What does she wish competitors and viewers understood about the role?

“What they don’t understand is that they’re seeing a picture, but we’re getting the entire story, and we’re making the decisions based upon that story,” she said. “That can make a real difference. And we’re the ones putting ourselves out there to right a situation that’s been broken by players. We haven’t caused any distress. We’re there just to try and put it back together again.”

  • Interviews for this feature took place at the Pokémon world championships in San Francisco. The writer’s travel and accommodation expenses were met by the Pokémon Company.

Explore more on these topics


Source: Technology

‘This gap opens up of doubt and scepticism about everything’: Jess and Morgs confront the politics of deepfakes

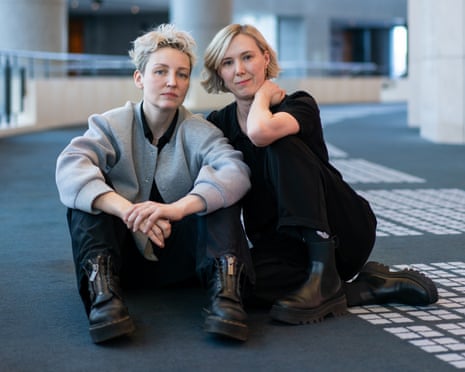
Choreographers Jessica Wright and Morgann Runacre-Temple sit together on the floor

‘It’s really about the strange shifting relationship with the landscape of truth’ … Morgann Runacre-Temple and Jessica Wright. Photograph: Yonathan Kellerman

‘It’s really about the strange shifting relationship with the landscape of truth’ … Morgann Runacre-Temple and Jessica Wright. Photograph: Yonathan Kellerman

‘This gap opens up of doubt and scepticism about everything’: Jess and Morgs confront the politics of deepfakes

In the choreographers’ new work, virtuosic movement and some green-screen magic unfurl the theatricality of high-stakes television interviews

It appears the interviewer has got him on the ropes. “For the record, I did not take part in a pagan ceremony with minor members of the royal family in which we daubed ourselves in paint,” states the beleaguered politician, caught outside Buckingham Palace with his flies undone and forced to defend himself. This is a fabrication, of course – I’m watching the scene play out in an east London dance studio – but it doesn’t feel miles away from something that could be true. And how do we know what’s the truth anyway? That’s the question in Deepfake, the latest piece from award-winning dance duo Jessica Wright and Morgann Runacre-Temple, AKA Jess and Morgs.

The pair tell modern stories with ambitious tech – film and live camera work – and often techy themes, too. “We’ve always been drawn to where there’s a crossover between the theme and the form,” says Runacre-Temple. “What gets us excited is seeing the contemporary world reflected back.” The pair scored a massive hit with their 2022 piece Coppélia, made for Scottish Ballet, which turned a twee 19th-century ballet about a dancing doll into a cautionary tale of AI automatons and unrestrained tech bro egos. Definitely not one-hit wonders, earlier this year they made their debut at the highly esteemed Paris Opera Ballet.

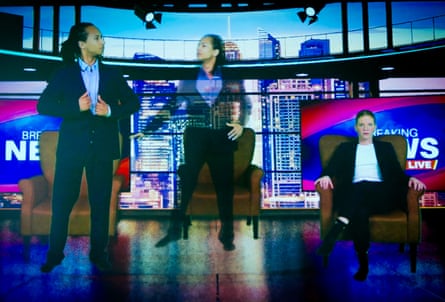
Gladiatorial drama in smart tailoring … Deepfake. Photograph: Chewboy

Deepfake is set in a green-screen studio, where the interview is taking place between a cool-headed journalist and a politician. With writer Jeff James, Jess and Morgs looked at a wealth of TV interviews, from Jeremy Paxman’s 1997 grilling of Michael Howard, where he asked the same question 12 times, to the former prince Andrew’s disastrous turn on Newsnight. They also took inspiration from the current ultra-media-trained politicos who “continually and bombastically evade any questions at all”, says Wright.

They liked the way the television interview is already a theatrical setup, says Wright. “I think there’s something fun about putting that on stage and asking the audience to engage with the theatricality as well.” It’s gladiatorial drama in smart tailoring. “It’s really high stakes; it’s win or lose for both of them,” adds Wright.

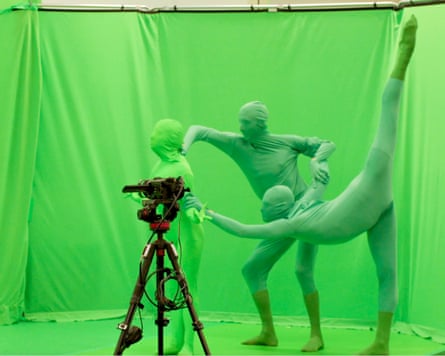
In the show, the interview will be filmed live by four cameras – then, as well as seeing what’s happening in reality, the audience will watch another version on screen with background footage edited in. We’ll be privy to the fabrication of the image and a number of possible realities. There are also seven dancers in green-screen suits who manipulate the environment but will disappear in the edit.

Privy to the fabrication of the image … Deepfake. Photograph: Chewboy

As Runacre-Temple says, green screen can actually look quite lo-fi – “It’s got that slightly absurd, playful, silent movie quality about it” – and it’s ancient tech compared with the kind of AI deepfakes that are emerging today. “They look so hyper real,” says Runacre-Temple. “The danger of deepfakes is not only that people believe things that aren’t true to be real, but that they start to disbelieve things that are true, and this gap opens up of doubt and scepticism about everything.” Or, as in their story, someone who has been caught out doing something they shouldn’t can insist it’s a fake image. “It’s really about the strange shifting relationship with the landscape of truth.”

I go to visit rehearsals on a day when there’s no tech in sight, bar a couple of laptops. “It’s good to go analogue to actually finish the choreography,” says Wright, wryly, counting the diminishing days to the premiere. All we have is an enormous studio and two incredible dancers: Rebecca Bassett-Graham, best known for dancing with Wayne McGregor’s company, who is playing the journalist; and as the politician, Kennedy Junior Muntanga, who has worked with Akram Khan.

‘It’s got that slightly absurd, playful, silent movie quality about it’ … Deepfake. Photograph: Chewboy

The text plays in voiceover while the two dancers embody and expand on its meaning. Their quick-fire movements visualise all the dynamics of a charged conversation: charm, challenge, cooperation, accusation, entrapment, etc. The feel is freewheeling, but each movement is tightly mapped to the syllable, every flex of muscle is considered. In certain scenes with the green screen, dancers will have to hit exact marks and even eyelines on exact words “or the whole illusion collapses”, says Wright. They’re creating their own high-stakes environment for the performers, where “the dancers’ virtuosity is a metaphor for these very virtuosic performances in interviews”.

Will this battle have a winner? Can we believe what we see? Jess and Morgs aren’t giving any spoilers. “Hopefully it will be surprising and mischievous,” says Runacre-Temple.


Source: Technology

Nick Clegg plays down fears ‘godlike’ AI could exterminate humanity

Clegg gesturing while speaking in 2022 with Meta logo behind

Nick Clegg, who stepped down from Meta in 2025, said one person who runs an AI lab told him the current discourse was ‘totally silly’. Photograph: Kenzo Tribouillard/AFP/Getty Images

Nick Clegg, who stepped down from Meta in 2025, said one person who runs an AI lab told him the current discourse was ‘totally silly’. Photograph: Kenzo Tribouillard/AFP/Getty Images

Nick Clegg plays down fears ‘godlike’ AI could exterminate humanity

Former deputy PM now involved in tech industry says many within sector are ‘winding themselves up into a lather’

Nick Clegg has dismissed fears over AI’s “godlike power to exterminate humanity”, calling it a sign that tech bosses are “breathing their own fumes”.

The former UK deputy prime minister said that tech bosses should focus on addressing known specific threats such as cybersecurity and bioweapons rather than the “slightly hand-wavy view that this technology is unavoidably going to develop some godlike power which is going to turn on us and exterminate humanity”.

Speaking to BBC Radio 4’s Today programme, he said: “I think it is perhaps accidentally self-serving, because it sort of implies that we can only be made safe by having everything controlled, in effect, by an oligopoly of a small number of companies, and I think it slightly paralyses the political debate.”

Clegg, who was formerly the president of global affairs at Meta and owns more than 917,000 shares in Nscale, a UK-based datacentre, and is a cofounder of the AI startup AMI Labs, said he spent “a huge amount of time” with people in the tech industry.

“They don’t agree amongst themselves at all. Of course, we hear the most apocalyptic voices,” he said, noting that one person who runs an AI lab said the current discourse was “totally silly”.

“There is a culture in Silicon Valley – it’s an odd place for those who haven’t been there. It is in many ways the centre of the universe, or at least claiming to shape it. It’s also an oddly parochial place. It’s a strange sort of culture where the engineers can get quite close to the technology and start slightly breathing their own fumes as they wind themselves up into a lather about these things,” he said.

Asked about the autonomous hack conducted by a group of OpenAI agents on a major real-world company, Hugging Face, Clegg said there was a case for “tramlines and greater transparency”.

However, he said this would be unlikely to happen under a Trump administration given its competitiveness on AI. He also suspected China’s cooperation would be limited, since the development of AI technologies was viewed as a “national mission” after the country was “cheated out of the Industrial Revolution”.

He added: “I think there’s a great potential for the big three techno democracies in the world – India, Europe and the US – to collaborate more.”

skip past newsletter promotion


Asked whether the British prime minister, Andy Burnham, could take a lead on such efforts, Clegg noted the UK was not a world leader on AI: “We need to be realistic about what influence we can and cannot exert.”

Clegg also disagreed with other proposed remedies, such as introducing a “kill switch”, which he said would be unworkable; or only producing closed models, where source code is not made public, which he said were no safer than open source models according to the evidence.

Instead, he suggested: “There is a lot that can be done both voluntarily and through regulation, to enforce far greater transparency on the way in which these models are concocted and how they operate.”


Source: Technology

Two-Tier Encryption in the UK – Identical Apple Devices, Different Protection

Here’s something odd. Alice and Bill both live in the UK. Both have identical iPhones. Both use iCloud. Both pay Apple for the same services. Alice has Advanced Data Protection switched on, protecting the majority of her iCloud data. Bill doesn’t, and can’t switch it on. Alice enabled it before Apple withdrew the feature for new UK users in February 2025. Bill missed the window.

To understand how this happened, we need to go back over a decade to the aftermath of the Snowden/NSA revelations surrounding PRISM. In January 2014, Tim Cook was interviewed by David Muir for ABC News. Cook said, “We have a gag order on us right now,” but clarified, “there is no back door. The government doesn’t have access to our servers. They would have to cart us out in a box for that… we feel that strongly about it.”

Nearly two years later, on the 2nd of December 2015, Syed Rizwan Farook and Tashfeen Malik carried out the San Bernardino terrorist attack, killing 14 people and wounding 22. The FBI obtained the iPhone 5C that had been used by Farook. They had a warrant to search the iPhone, but they didn’t know the passcode. The FBI obtained a court order to compel Apple to help them into the device. They wanted Apple to create a version of iOS that would remove or circumvent the iPhone’s security protections (in particular the limits on passcode attempts). Apple demurred. In an open letter by Tim Cook, he said that the government was asking for something the company simply didn’t have, and something it considered “too dangerous to create.”

In another interview with ABC’s David Muir, Cook gave an impassioned and at times angry defence of Apple’s position, describing the requested software as the “equivalent of cancer.” He argued that such a tool would function as a “master key” capable of unlocking hundreds of millions of devices, and that once built, there would be no way to guarantee it was only used against that one phone.

In a separate interview for CBS’ 60 minutes, Cook reiterated the underlying principle: “If you put a back door in, then that back door is for everybody. For good guys and bad guys.” James Comey, then Director of the FBI, told 60 Minutes that whilst he was committed to protecting the privacy of Americans, “the notion that we would market devices that would allow someone to place themselves beyond the law troubles me a lot.”

The FBI eventually obtained access using a third party (widely reported to be Cellebrite [1]) and withdrew its legal action against Apple.

Skip forward almost a decade, and on the 7th of February 2025, The Washington Post exclusively revealed that the UK government had ordered Apple to provide access to data protected by its strongest level of iCloud encryption. The UK has powers to make such requests under the Investigatory Powers Act 2016 — the centrepiece of the UK’s modern surveillance law. [2]

One of the mechanisms available under that legislation is called a Technical Capability Notice (a sanitised, bureaucratic euphemism if ever there was one). A Technical Capability Notice (TCN) is a legal instruction that requires a communications / technology provider to maintain or develop the capability to comply with certain requirements (the notice itself doesn’t authorise access to anyone’s data — it just ensures the capability exists for when a specific warrant or authorisation does). Before issuing a TCN, the government is obliged to consider things such as technical feasibility, cost, likely benefits and the number of users affected. A TCN requires approval from a Judicial Comissioner, and the recipient of a TCN is generally gagged from revealing its existence or contents without the UK Secretary of State’s permission (the Home Office says it will generally neither confirm nor deny whether a particular TCN exists).

The Post reported that UK security officials had issued such a TCN, in secret, in January 2025, requesting that Apple create a way to access encrypted iCloud data belonging not just to UK users, but to Apple users worldwide. The chutzpah of it all was astonishing.

Apple’s position (privately, since they were prohibited from commenting publicly on the reported TCN) showed fidelity to its previous stance: deliberately weakening end-to-end encryption, for whatever purpose or for whomever the intended beneficiary, would make every user less secure. So the dispute became the UK government saying it needed access, Apple saying it couldn’t decrypt the data, and the UK effectively replying: then change the system so that you can.

It’s important to get into the technicalities here. All iCloud data is encrypted. But there’s a difference between encrypted and end-to-end encrypted (E2EE) data. iCloud already protects sensitive categories of data (like Passwords, Health data, Messages in iCloud, etc) with end-to-end encryption by default. For everything else, Apple retains the ability to decrypt the data when necessary, and can be ordered to hand this data over by law enforcement. With Advanced Data Protection (ADP), several more categories of iCloud data become end-to-end encrypted (iCloud Backup, Photos, Notes, and others). Apple itself doesn’t possess the keys needed to decrypt that protected data. It’s not something Apple can unlock just because a government asks for the contents.

There was a heartening backlash to what the UK government had asked Apple to do. The Investigatory Powers Tribunal (IPT) became involved (the independent UK body that hears complaints about unlawful surveillance or human rights breaches by public authorities). Privacy International and other groups argued that the government shouldn’t be able to secretly compel technology companies to weaken encryption without adequate public scrutiny. Apple itself effectively confirmed the underlying confrontation with the UK government, without directly acknowledging the existence of the reported TCN: on the 21st of February it announced that Advanced Data Protection would no longer be available to new UK users, stating that “we have never built a backdoor or master key to any of our products or services and we never will”. [3]

To be clear, the reported TCN itself didn’t order Apple to withdraw ADP. It ordered Apple to maintain the technical capability to make ADP-protected data accessible when a warrant required it. If Apple had complied with the reported TCN, they would have needed to create a mechanism capable of unlocking private information that could potentially be exploited by hackers, hostile governments, and others. It would also, I believe, have set a dangerous precedent — the “good guys” might not actually be good, and even if they were, a future government might not be, and might want to use that access for bad ends. Apple was the canary in the coal mine in this case. [4] Such a precedent would also affect WhatsApp, Signal [5], cloud-storage companies, password managers, banks, and essentially any service relying on genuine end-to-end encryption.

Faced with a legal order that would have required it to change the security architecture on which ADP depended, Apple found a third option: stop offering the feature that made this dilemma exist in the first place. It reverted affected UK iCloud data to Standard Data Protection, where Apple does hold the keys and can respond to lawful legal procress (except the baseline categories that stay end-to-end encrypted either way). This satisfied the underlying legal requirement without ever building a ‘backdoor’.

Apple said the decision to withdraw ADP in the UK left them “gravely disappointed”. There was, however, an important disclaimer. Apple only stopped allowing new UK users to turn on Advanced Data Protection. It said it could not automatically disable ADP for existing users who had already turned it on. Why couldn’t Apple just switch ADP off for everyone in the UK? Because Apple deliberately designed ADP so that the setting can only be changed by the user’s trusted devices. Apple’s security documentation says its servers can’t modify the ADP setting, or roll it back on a user’s behalf.

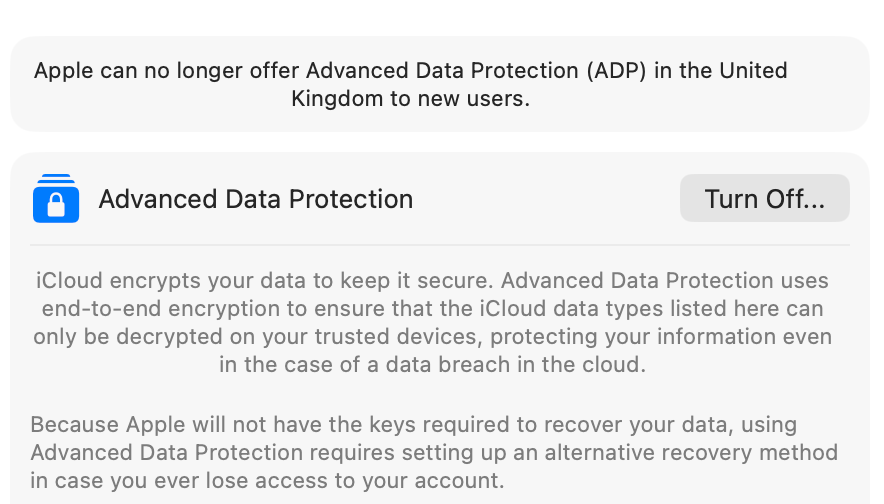
This has effectively led to a “two-tier” level of encryption for Apple customers in the UK. People like myself, who were fortunate to have enabled the feature before it was pulled, are still protected by Advanced Data Protection. Apple says “users will be given a period of time to disable the feature themselves to keep using their iCloud account” (the company hasn’t published a deadline for when existing UK users must do this). People who didn’t have ADP turned on prior to the decision, or became Apple customers after the company pulled the feature, can’t turn ADP on.

This is what I still see on my iPhone:

Screenshot 2026-09-14 at 15.24.32.png

To bring this into sharper focus: Alice enabled ADP on her iPhone in 2024. Bill can’t turn the feature on. Both are UK residents. Both use iCloud. Both are subject to the same UK legal regime. Yet Alice has the stronger end-to-end encryption for the additional ADP-protected categories, while Bill does not.

There are two ways Bill might have ended up here. Maybe he bought his iPhone after Apple pulled the option for new UK users entirely. Or maybe he bought it before the cutoff, like Alice, but didn’t know that ADP was an opt-in feature — he had to actively turn it on, and he didn’t. Whichever version of Bill you imagine, the same fact now applies to both: it’s too late for him to do anything about it.

Tough luck, Bill.

Where things stand now, and why the secrecy matters.

The UK government’s original reported demand was global. It was replaced in late 2025 by a narrower notice affecting only UK citizens, after the Trump administration applied pressure over concerns about the implications for American users.

In July 2026, Apple lodged a fresh complaint at the Investigatory Powers Tribunal, which became public the following month. Then, on the 11th of September 2026, U.S. Senator Ron Wyden [6] (a Democrat) and Republican Congressman Warren Davidson called on the UK’s Investigatory Powers Tribunal to open up its proceedings concerning Apple’s encrypted-data dispute. In their letter to the tribunal, they argued that the UK’s demand for secrecy undermines democratic governance on both sides of the pond, warning that Congress cannot fulfil its oversight duties if “foreign non-disclosure orders are weaponized” to stop US companies answering to elected lawmakers.

On the 17th of September The Daily Telegraph reported that Apple had asked the Investigatory Powers Tribunal to remove restrictions that gag them from confirming the existence of the reported TCN. Daniel Beard KC, representing Apple, told the tribunal this would allow “facts to be deployed in the open”. Lawyers for two human-rights organisations — Liberty and Privacy International — argued that maintaining the gag order is “farcical”, because everyone knows about it anyway; Ben Jaffey KC compared the secrecy order to the “emperor’s new clothes… and brings the administration of justice into disrepute”.

And this is the most troubling aspect of this whole sorry affair — the secrecy. Technical Capability Notices can be issued by the UK government in secret, and the recipient of the notice is restricted in law about what it can publicly say about it.

In a 1961 speech to the American Newspaper Publishers Association [7], John F. Kennedy warned that “the very word ‘secrecy’ is repugnant in a free and open society,” specifically highlighting “secret societies… secret oaths and… secret proceedings”. He argued that a free society shouldn’t automatically accept secrecy just because the government invokes security. He cautioned that any announced need for increased security risked being exploited by those seeking to expand it into full-blown censorship and concealment.

I want to be fair to the UK government here, so let me try the most charitable explanation first: maybe this isn’t malice, just plain ignorance — technological illiteracy on behalf of UK government ministers. But this explanation is too simple, too comforting. It’s difficult to believe the UK government isn’t aware that encryption is not like a physical safe where the manufacturer holds a master key that a government can subpoena. The cryptographic design means there is no master key. You can’t obtain information just by ordering the manufacturer to hand it over. The only way to do it is to change the system. And ignorance becomes even harder to credit once you consider who would likely be involved in issuing a TCN — not just ministers, but security and intelligence agencies, lawyers and technical advisors, all operating within the statutory framework of the Investigatory Powers Act.

The government might argue this situation is nothing like the FBI’s 2016 demand for a master key: it’s a legal mechanism, subject to independent judicial oversight, targeted at serious crimes. But, to my mind, judicial oversight doesn’t solve the underlying technical problem — any mechanism that lets an authorised party in, is a mechanism an unauthorised party could potentially discover and exploit too. The UK government (and this behaviour concerns successive UK governments, of different political flavours, Labour and Conservative alike) seems to believe the national security benefits outweigh any cybersecurity cost. I do understand the position: serious criminals use encryption, therefore law enforcement needs a way of accessing encrypted material when legally authorised. But we are at a stalemate. Apple doesn’t have the decryption keys. It can’t give the government what it wants. So, in the context of this particular dispute, the UK government only really has two options: force Apple to change the system so that someone other than the user’s trusted devices can ultimately gain access — call it a backdoor, a technical capability, whatever euphemism suits — or accept that some data will stay permanently out of reach, inaccessible, as part of the trade-off of living in a free society.

I sometimes wonder what would have happened if Apple had acquiesced to the FBI’s requests in 2015. No matter what one thinks of Tim Cook’s (likely calculated) appeasement of Trump [8], it’s worth looking back at his fidelity to one unequivocal position after the San Bernardino terrorist attack, when he and his company came under significant fire, not just from the FBI and the wider apparatus of government, but from large sections of the public too. It remains one of the most prominent examples of a private American company publicly resisting government overreach on behalf of its users. [9]

Over on this side of the pond, Apple chose to resist the UK government’s original demand by withdrawing ADP from new UK users, ironically depriving them of end-to-end encryption for categories of iCloud data that ADP previously protected. It wouldn’t be fair to treat the resultant two-tier outcome as something Apple did to Bill. Apple was handed an extraordinarily difficult choice and picked the least-bad option available. In my view, the unfairness belongs with the government decision that created this impossible order in the first place.

Note: I wrote to the Home Secretary and other relevant ministers ahead of publishing this piece; none had responded by the time it went live.


  1. Researchers at the University of Toronto’s Citizen Lab have documented Cellebrite’s extraction devices being used against human rights activists and journalists in Russia, Serbia, and elsewhere, sometimes even after the company claimed to have cut off the country in question. ↩︎

  2. The roots of the Investigatory Powers Act go back to the 2012 ‘Snooper’s Charter’, an attempt to expand government access to communications data, and to earlier legislation such as the Regulation of Investigatory Powers Act 2000. After the 2012 proposals stalled, the Government returned with the Investigatory Powers Bill in 2015. It became law in November 2016 and came into force the following year. ↩︎

  3. Withdrawing ADP in the UK did not affect the 14 iCloud categories that were already end-to-end encrypted by default, including iCloud Keychain and Health. ADP increases the total from 14 to 23 categories. For UK users without ADP, the additional categories (iCloud Backup, Photos, Notes, iCloud Drive and so on) revert to Standard Data Protection. ↩︎

  4. Canaries sing constantly, and fall silent at the first hint of gas. Miners learned to listen for the silence. This isn’t the only warning system built around birdsong. Some 17th-century Japanese castles (Kyoto’s Nijō Castle, for example) have floors said to chirp like a nightingale with each footstep, which is popularly believed to have alerted guards to anyone creeping through the corridors (the castle’s signage. however, says: “The singing sound is not actually intentional, stemming rather from the movement of nails against clumps in the floor caused by wear and tear over the years”). ↩︎

  5. Signal Foundation’s president Meredith Whittaker has said, “We would leave the U.K. or any jurisdiction if it came down to the choice between backdooring our encryption and betraying the people who count on us for privacy, or leaving.” ↩︎

  6. This is not a new fight for Wyden — he’s been one of the loudest anti-backdoor voices in the U.S. Senate for the best part of a decade, introducing the Secure Data Act in December 2014 to ban the government from forcing companies to weaken encryption. ↩︎

  7. Kennedy gave this speech about a week after the failed Bay of Pigs invasion. He argued simultaneously for “far greater public information” and “far greater official secrecy”, reflecting the tension between press freedom and national security during the Cold War. ↩︎

  8. Tim Cook presented Trump with a custom 24-karat gold-based glass plaque in the Oval Office in August 2025, alongside a $100 billion manufacturing investment announcement. ↩︎

  9. A couple of other notable examples: Lavabit shut itself down entirely rather than hand the FBI its SSL keys, after being threatened with a $5,000-a-day fine; Yahoo fought a secret FISA court order demanding it hand over user data for the NSA’s PRISM program, and was threatened with fines of $250,000 a day for refusing. ↩︎


Source: Hacker News

Latest Posts